The SSLv3 protocol is disabled in Windows by configuring Registry keys and values.
SSLv3 and the older SSLv2 protocols are both vulnerable by their implementation and should now be disabled. Newer protocols are available for use.
Open the Registry editor with the command regedit.exe. Changes to the Registry can make your computer unusable, proceed with care and preferably make a backup of the registry before making any changes.
After completing this task the computer will need to be rebooted.
In the Registry navigate to:
HKEY_LOCAL_MACHINE > SYSTEM > CurrentControlSet > Control > SecurityProviders > Schannel > Protocols
At this point a new sub-key is added for the protocol.
Right click on Protocols and from the pop-up window select New followed by Key. For the Key name enter SSL 3.0
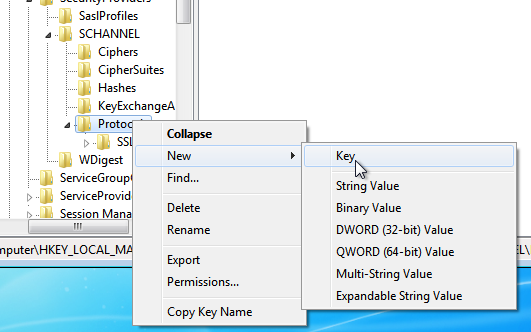
To be added below this key are additional keys for Server (and later Client). Add the Server key as above.
A new DWORD is to be added under the Server key.
Right click on SSL 3.0, in the left navigation tree and select New followed by DWORD. Give it the name of Enabled with a value of 0.

If you wish to block the protocol on the client side too then add the DWORD DisabledByDefault with a value of 0.
This is illustrated in the image below which shows the addition of a Client key below the SSL 3.0

Just as the additional registry keys have been added to control the use of the SSLv3.0 protocol the same may be done for the earlier SSLv2.0 protocol. In the image above the entry for SSL 2.0 is shown.